Scope
This transaction is used by the X-Service User to pass a claimed identity assertion (a SAML 2.0 token) to the X-Service Provider.
Unlike most ITI transactions, ITI-40 is never invoked as a standalone exchange. It is carried inside the WS-Security header of the other transaction it secures (e.g. ITI-38, ITI-39 and RAD-75)
Use Case Roles
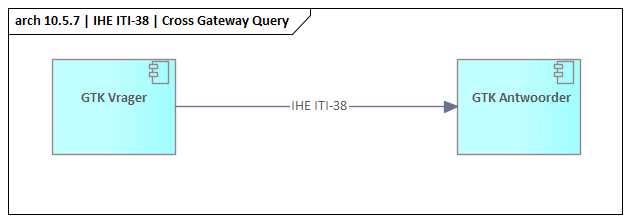
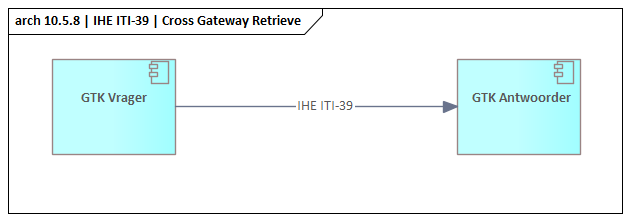
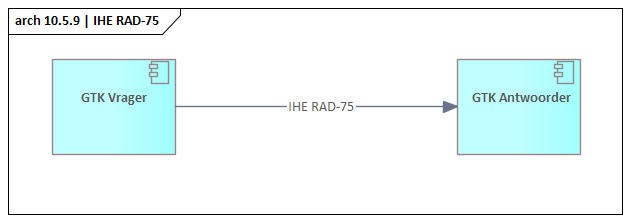
This transaction uses SOAP v1.2 and Synchronous Web Services.
Referenced standards
Implementers of this transaction shall comply with all requirements described in Web Services for IHE Transactions.
|
ebRIM |
OASIS/ebXML Registry Information Model v3.0 |
|
ebRS |
OASIS/ebXML Registry Services Specifications v3.0 |
|
ITI TF-3:4 |
Metadata used in Document Sharing profiles |
|
MTOM |
SOAP Message Transmission Optimization Mechanism http://www.w3.org/TR/soap12-mtom/ |
|
SAML 2.0 |
OASIS Security Assertion Markup Language v2.0 |
|
WS-Security |
OASIS Web Services Security: SOAP Message Security 1.0/1.1 |
|
XML-Signature |
W3C XML Signature Syntax and Processing |
|
XML-Encryption |
W3C XML Encryption Syntax and Processing (if confidentiality option used) |
|
ATNA |
ITI TF-2: Authenticate Node [ITI-19] — required grouping for secure transport |
Messages
Cross Gateway Retrieve
For more technical specification, see the original document: https://profiles.ihe.net/ITI/TF/Volume2/ITI-40.html
NB: NB: This transaction is always carried inside another transaction's WS-Security header — it is not sent independently. Transactions it is commonly grouped with include:
-
ITI-38 (Cross Gateway Query)
-
ITI-39 (Cross Gateway Retrieve)
-
RAD-75 (Cross Gateway Retrieve Imaging Document Set)
NB: All transactions are logged with an ITI-20 audit transaction, see IHE:ITI volume 2 for the correct implementation.”